Got some questions about complying with the FCC’s new cybersecurity requirements by the Sept. 29 deadline?
A new FAQ from the commission may help.
For example, do the new security password requirements apply to all broadcaster equipment, or only to EAS devices, or to all IP-connected equipment in the program chain?
“The password requirements do not apply to all broadcaster equipment or all IP-connected equipment in the program chain,” the commission wrote.
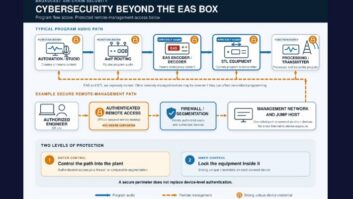
“The password requirements only apply to EAS equipment, studio transmitter link equipment and any remotely managed equipment that routes, processes or inserts content into the program stream transmitted by the EAS participant to the public and subscribers (e.g., audio processors; ad insertion systems; and AM and FM radio and DTV transmitters that are remotely managed).”
Thus EAS participants must implement the new cybersecurity requirements for equipment beyond just EAS, but are not required to apply the requirements to remotely managed equipment that does not route, process or insert content into the program stream.
The FAQ answers common questions about passwords, firewalls and equipment no longer supported with software updates.
[Related: Cybersecurity Beyond the EAS Box]